HNHUSSAIN NAQVICYBERSECURITY LEADERSHIP
اردو

CYBERSECURITY · GOVERNANCE · RESILIENCE

Hussain
Naqvi.

Cybersecurity Leadership.
Enterprise Resilience.
Technical Depth.

Cybersecurity leader with 10+ years of industry experience across enterprise risk management, auditing, GRC, security architecture, IT/OT security and critical infrastructure protection.

● Karachi, Pakistan10+ years across cybersecurity, GRC & IT/OT
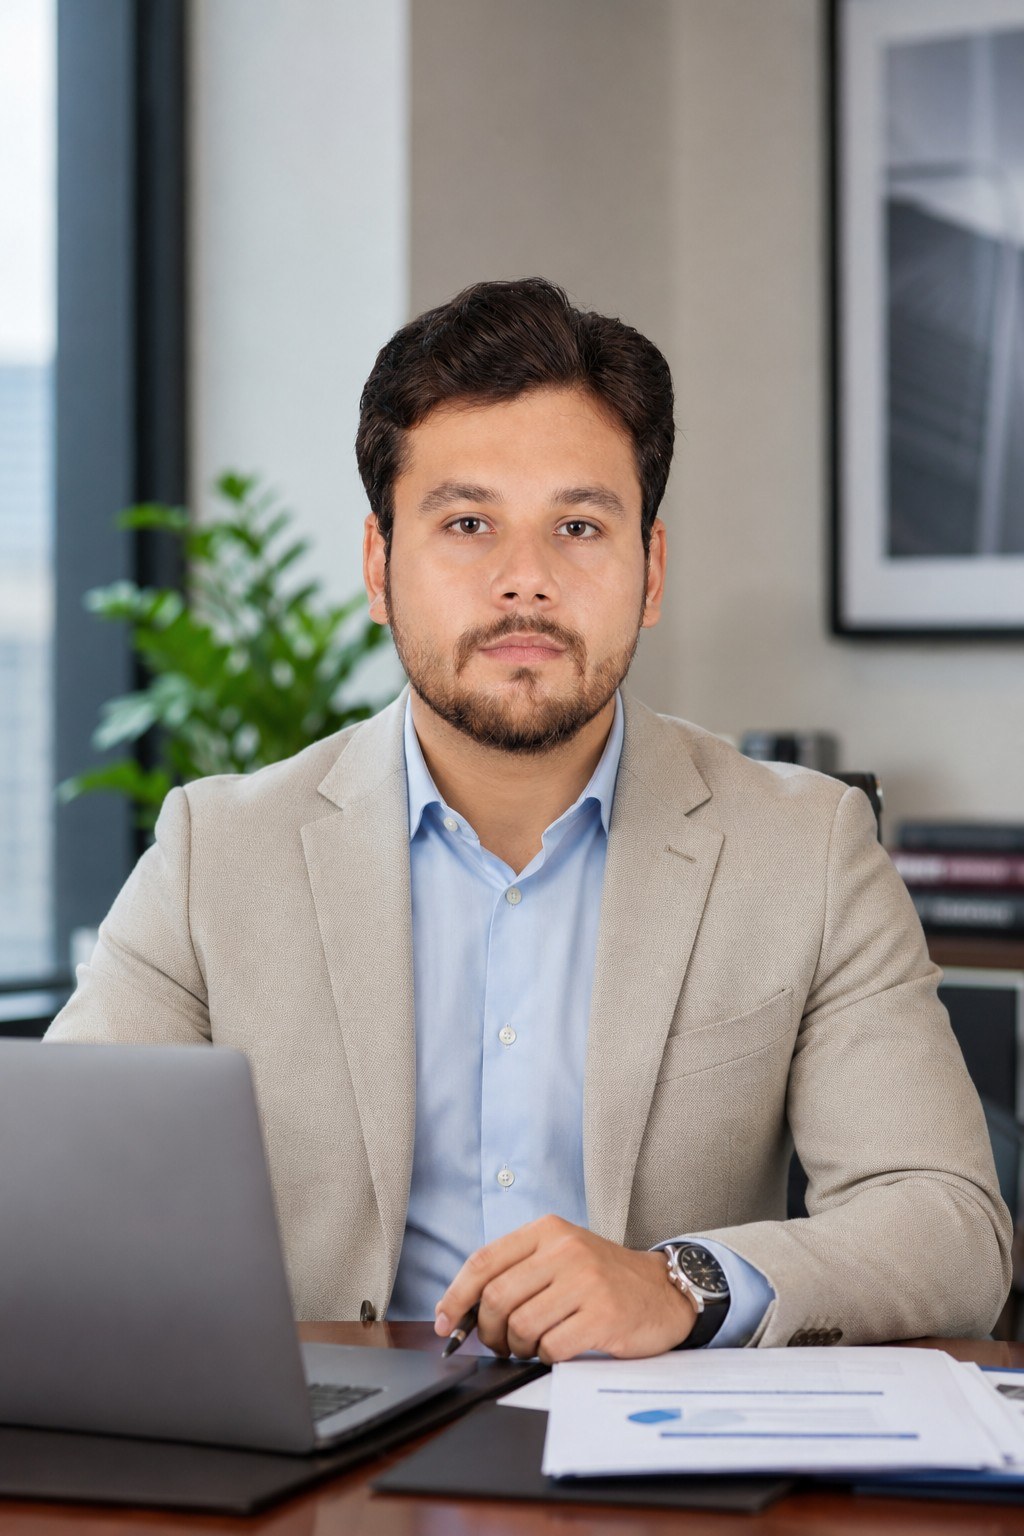
Hussain Naqvi in a light grey blazer and blue shirt in an office
PROFILE / SECURITY · STRATEGY · SYSTEMS
HNCYBER
SECURITY
STRATEGY THAT CONNECTS TO EXECUTION SCROLL TO EXPLORE ↓
39%Reduction in major audit non-conformities
29%Reduction in compliance gaps
30%Improvement in project-delivery timelines
72+Cybersecurity policies, programs and SOPs

A PRACTICAL, RISK-DRIVEN APPROACH

Security is not a checkbox.
It is an operating discipline.

I work at the intersection of cybersecurity leadership, enterprise governance, and technical operations. My experience spans security strategy, risk management, audit readiness, SOC operations, vulnerability management, and infrastructure security. My approach is practical and risk-driven: understand the technology, identify exposure, implement appropriate controls, monitor continuously, and build governance that supports long-term resilience.

WHERE I CREATE VALUE

Strategic oversight.
Technical understanding.

Cybersecurity Strategy
Governance, Risk & Compliance
ISO/IEC 27001
NIST Cybersecurity Framework
Cybersecurity Audits
SOC & SIEM
Incident Response
Vulnerability Management
Security Architecture
IT Infrastructure
Security Policy Development
Team & Vendor Leadership

CAREER TIMELINE

Leadership built on
hands-on foundations.

Head of Cybersecurity

Dec 2022 — Present

Enterprise cybersecurity, GRC and critical infrastructure resilience

  • Lead enterprise cybersecurity strategy, governance, risk, compliance and cyber-resilience initiatives.
  • Lead a 20-member security function across security operations, GRC, infrastructure security and administration.
  • Lead biannual integrated cybersecurity risk assessments and treatment activities; oversee enterprise vulnerability management and risk-based remediation.
  • Direct security monitoring, threat detection and operational response, integrating monitoring, detection, response and governance processes.
  • Authored and operationalized 72+ cybersecurity policies, programs and SOPs.
  • Direct annual internal cybersecurity/IS audits and coordinate external audit engagements.
  • Contributed to a 39% reduction in major audit non-conformities and a 29% reduction in compliance gaps.
Head of IT Operations and Systems

Sep 2018 — Nov 2022

Infrastructure operations and operational security

  • Led enterprise IT operations across networks, systems, software, databases and configuration management.
  • Led and mentored a cross-functional team of eight engineers, technicians and administrators.
  • Managed infrastructure budgets and key technology-vendor relationships.
  • Performed patching, firewall configuration, incident triage and risk-impact analysis.
  • Reduced reported infrastructure downtime by 24% and improved project-delivery timelines by 30%.

Cloud Infrastructure Engineer

Feb 2016 — Jan 2017

Cloud hosting and infrastructure engineering

  • Administered Citrix XenServer, XenDesktop/XenTools, Linux and Windows Server environments.
  • Designed infrastructure solutions and managed web, DNS, FTP and mail services.
  • Administered Plesk and cPanel hosting environments.
  • Implemented centralized logging and monitoring using ELK Stack and LogAnalyzer.

FULL CAREER DETAILS

Prefer the concise version?

Download the three-page resume for career history, education, credentials and selected achievements.

Download PDF ↓

SELECTED DEMONSTRATIONS

Ideas made tangible.
Controls made practical.

Independent demonstrations across governance, defensive operations, automation and authorized lab testing. These visuals use illustrative data and do not represent employer systems.

ⓘ Portfolio demonstrations are conceptual or lab-based and use synthetic or illustrative data. No production deployment is implied.

EDUCATION, CREDENTIALS & RECOGNITION

Engineering foundations.
Leadership in a critical sector.

Education

B.E., Computer and Information Systems EngineeringNED University of Engineering and Technology · First Division2012–2015

Certifications & licenses

Critical Infrastructure Protection — OPSWAT · Jun 2026
Certified Security Analyst (ECSA) — EC-Council · Aug 2026
AI Ethics, Risk and Compliance — Charles Sturt University · Mar 2026
Certified in Cybersecurity (CC) — ISC2 · Nov 2025
AI Security and Governance Certified — Securiti.AI · May 2025
Strategic Cybersecurity Management — AttackIQ · Dec 2024
Fortinet NSE 1–3 Certified in Cybersecurity · Nov–Dec 2024
ISO 27001 ISMS Associate — SkillFront · Nov 2024

Recognition & awards

Leadership in Cyber Security Governance — Digital Pakistan Innovators (May 2026)

Volunteer & early leadership

Global Volunteer — ISACA (Jun 2026–Present)

Technical Director — NED Entrepreneurship Society (Mar 2013–Mar 2015)

Web Engineer — ASHRAE NED Chapter (Jul 2013–Sep 2014), supporting a 200+ member community

NOTES & PERSPECTIVES

Thinking beyond
the control checklist.

OCT 18, 2026 · GOVERNANCE

Building Cybersecurity Governance That Works

Connecting policy with operational practice, repeatable evidence, accountable ownership and measurable resilience.

Read the blog ↗

Future articles can be published directly on this website; existing LinkedIn writing can be linked or migrated after review.

LET'S CONNECT

Good security starts
with a conversation.

For professional collaboration, cybersecurity discussions, and speaking or writing opportunities.